If you read the June issue, you know the three network scanners 45+ ransomware groups reach for during discovery: SoftPerfect NetScan, Advanced IP Scanner and Advanced Port Scanner.

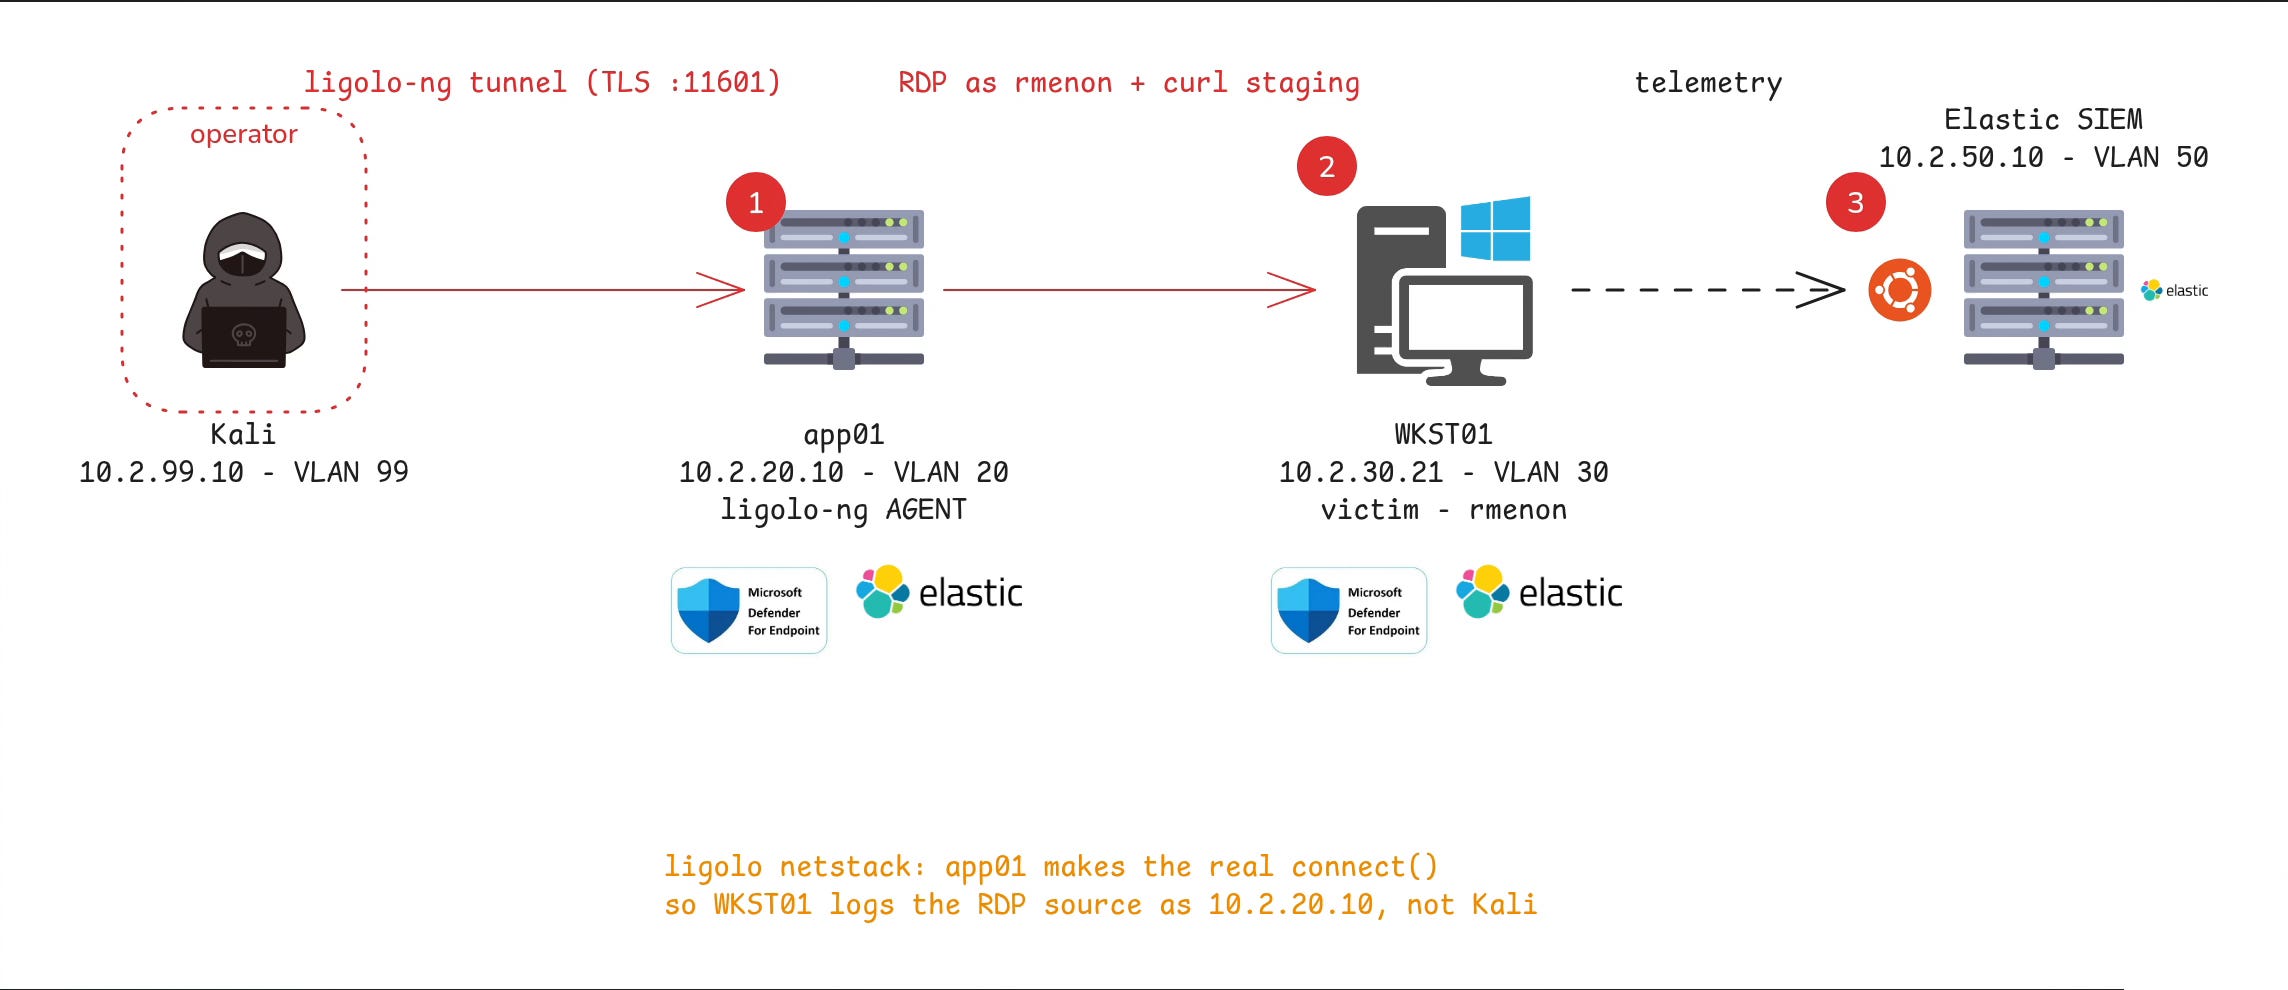
For the video I ran the scan again, this time through a ligolo-ng pivot.
What the video adds over the issue:
The scan landing in Defender Advanced Hunting (KQL), and the same sweep in Elastic ES|QL.
How I tell an admin running a scanner from an operator doing discovery.
A pivot trap: the operator came in through a ligolo-ng tunnel, so the victim logged the pivot host as the RDP source, not the attacker’s machine.