If you read the ScreenConnect investigation, you saw how one signed client got the attacker in and a second called a server they controlled.
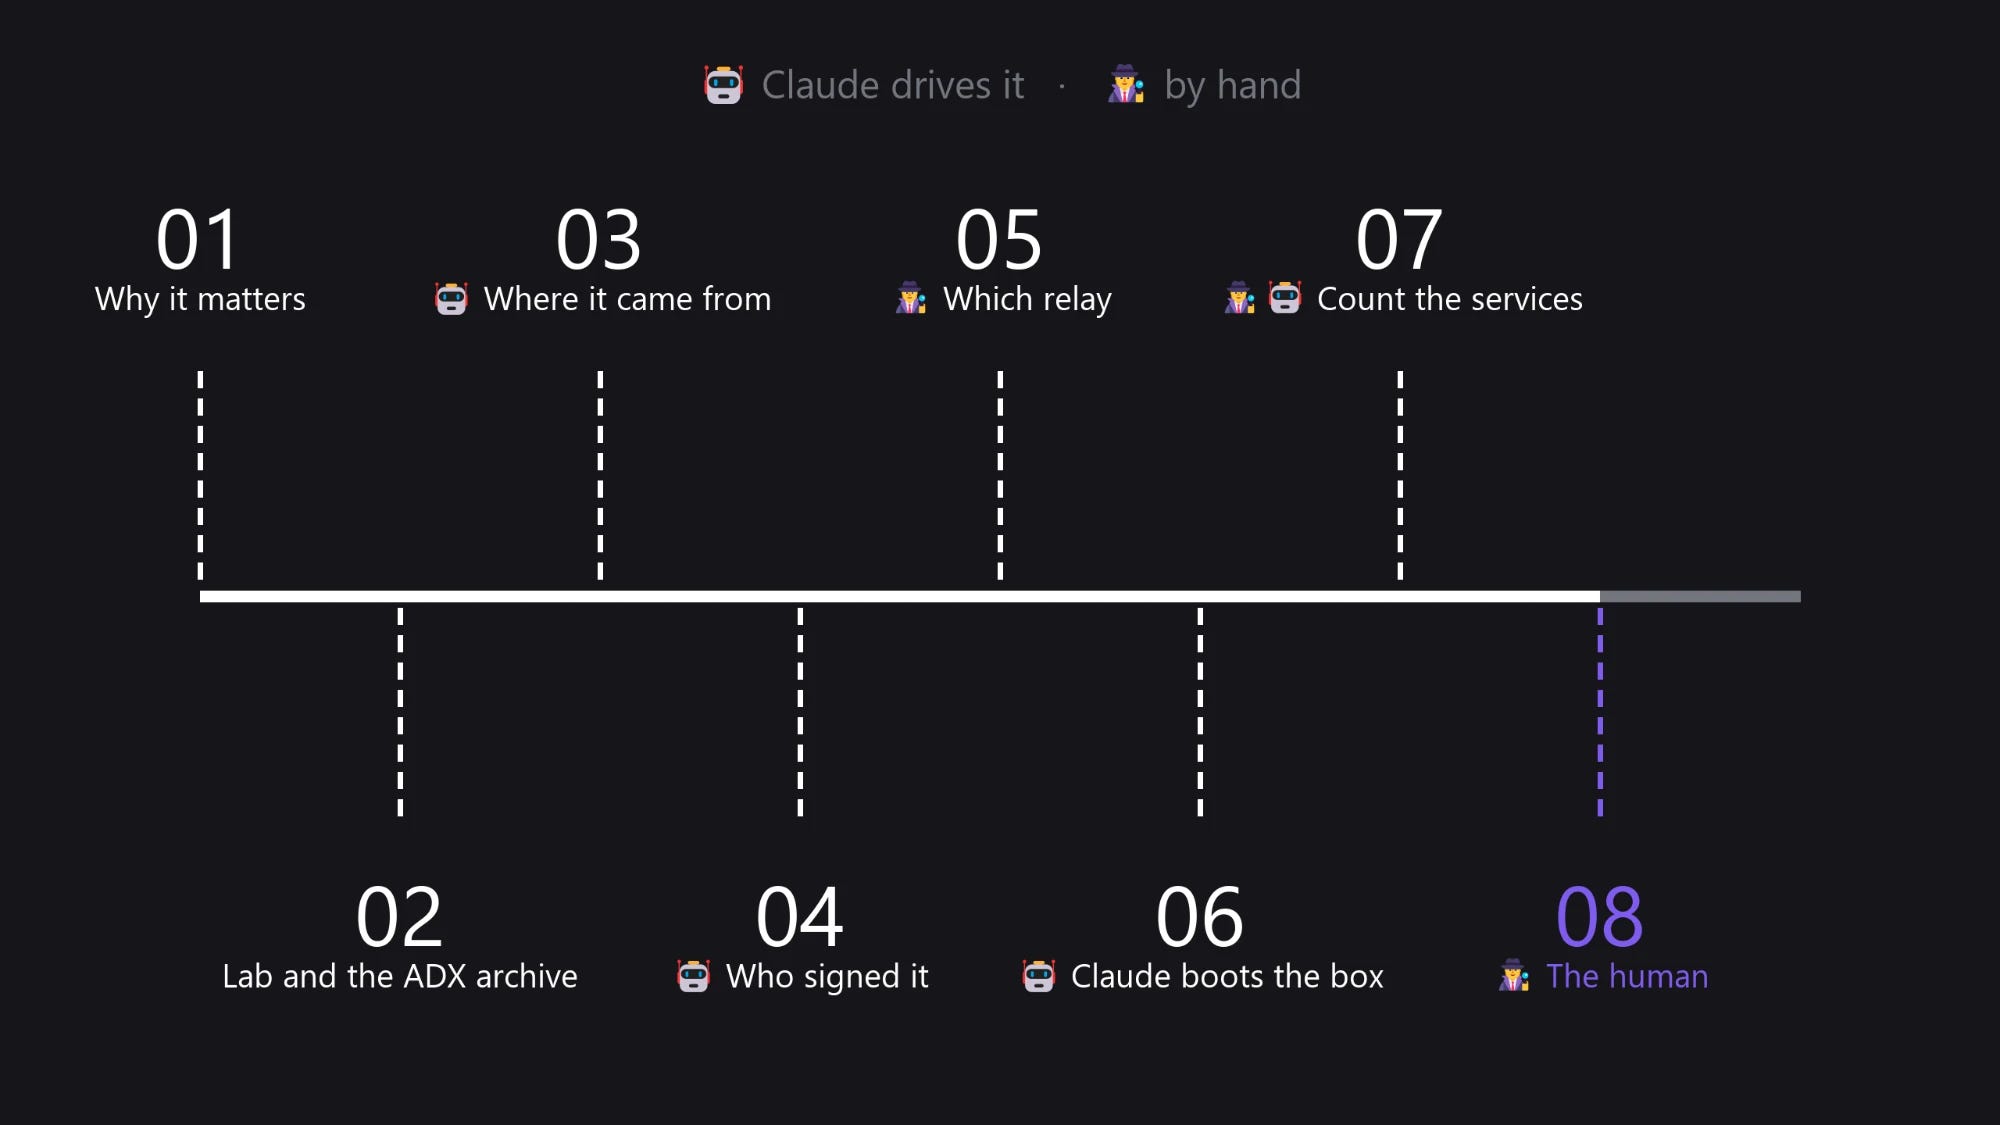
For this video I hunted both again, with Claude Code running part of the hunt and every row checked by hand.
What the video adds:
The Claude Code workflow across archived Defender telemetry in ADX (KQL) and Elastic (ES|QL), with the manual checks marked.
Both ScreenConnect client folders on disk, viewed from a snapshot booted offline.
Counting both ScreenConnect services and comparing their relays, so removing the first client doesn’t leave the second behind. Multiple instances still need context.