Securityinbits
Subscribe
Sign in
Home
Notes
Archive
About
Load Real Defender Telemetry into a Free ADX Cluster in One Paste
No tenant, no Azure subscription, no credit card. Eight MDE tables from a real lab intrusion, loaded with one script, checked against known row counts.
Oct 28
•
Ayush Anand
1
September 2026
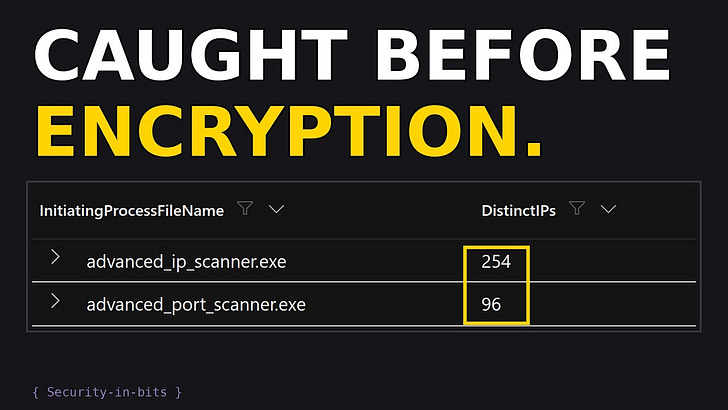
Watch it run: the network scan 45+ ransomware groups use
Catch the scan before the encryption. On real lab telemetry, in Defender and Elastic.
Sep 30
•
Ayush Anand
1
1
ScreenConnect RMM Abuse: The Cloud Client Gets In, The Self-Hosted One Stays
Two real samples in my lab dropped two implants on one host. One vendor-signed and loud, one self-hosted and configured to be invisible. Here is how to…
Sep 23
•
Ayush Anand
2
2
July 2026
32 Ransomware Groups Abuse AnyDesk. Your EDR Sees a Legit Tool
Is That AnyDesk Legit or Planted? A Lab-Validated Hunt
Jul 29
•
Ayush Anand
6
June 2026
Detecting Reverse SSH SOCKS Tunnels: Separating Benign -R From Akira Pivoting
Your EDR sees one process: ssh.exe. Here's how to read the shape it leaves behind.
Jun 17
•
Ayush Anand
1
2
Hunt Ransomware Before It Encrypts: The Three Tools 45+ Gangs Reach For
Six queries for MDE and Elastic that catch NetScan, Advanced IP Scanner, and Advanced Port Scanner pre-encryption.
Jun 6
•
Ayush Anand
2
7
This site requires JavaScript to run correctly. Please
turn on JavaScript
or unblock scripts